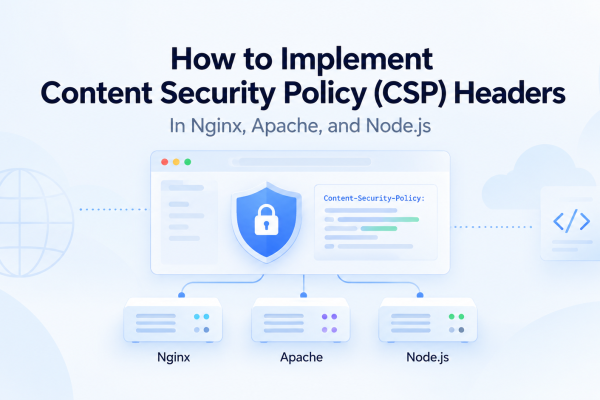
How to Implement Content Security Policy (CSP) Headers in Nginx, Apache, and Node.js
Content Security Policy often enters an enterprise backlog as a security-header task. It rarely stays that simple. A modern enterprise application may load JavaScript from multiple internal domains, analytics platforms, identity providers, CDNs, customer-support tools, payment systems, experimentation platforms, and increasingly AI-enabled services. Add legacy inline scripts and multiple deployment layers, and a CSP that…