The Circuit Breaker Pattern: Preventing Cascading Failures in Distributed Web Systems
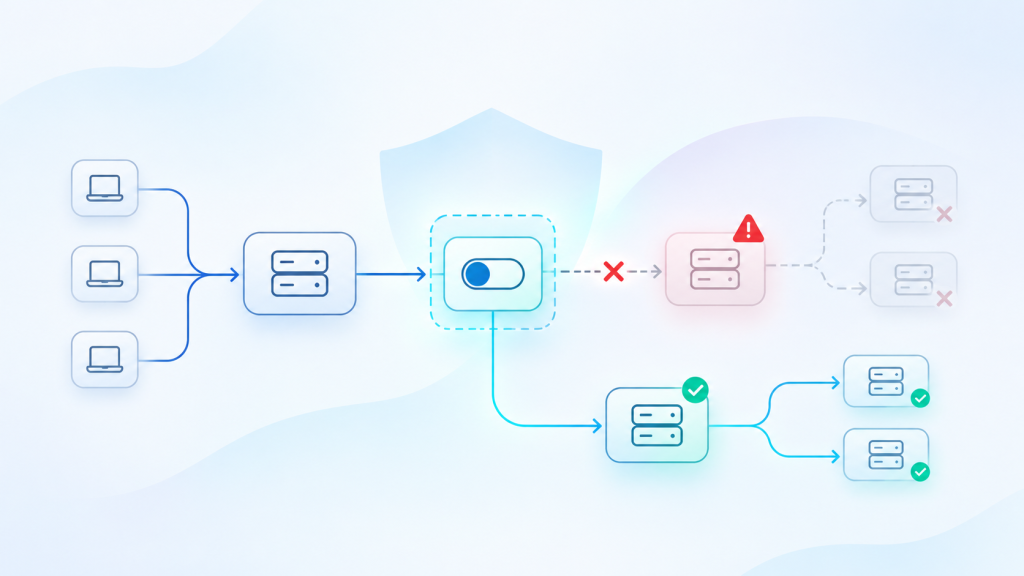
A distributed web system rarely fails because one component stops working. It fails because the…
A distributed web system rarely fails because one component stops working. It fails because the…

Database indexing problems rarely begin with an obvious outage. They usually appear as a checkout…
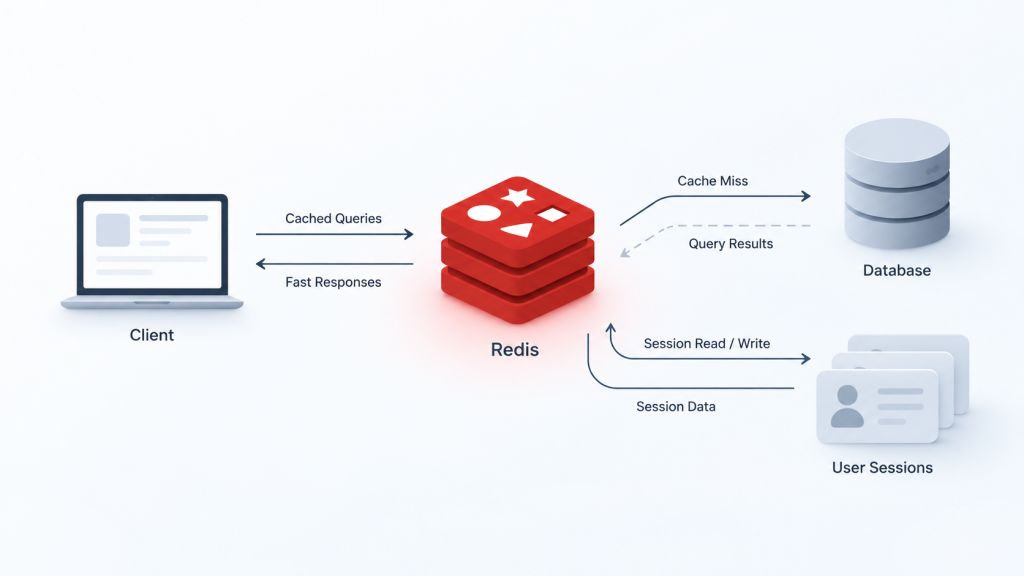
Enterprise applications rarely become slow because a database suddenly becomes incapable of returning data. Performance…
Enterprise web applications rarely become slow because of one badly written function or one undersized…

A distributed web system rarely fails because one component stops working. It fails because the rest of the system keeps behaving as though that component is healthy. A payment API becomes slow. An identity service starts timing out. A recommendation engine experiences database contention. Upstream services keep waiting, retrying, and occupying threads, sockets, connection pools,…

Database indexing problems rarely begin with an obvious outage. They usually appear as a checkout API that moves from 150 milliseconds to 700 milliseconds during peak traffic, a customer dashboard that becomes progressively slower as transaction history grows, or a database cluster that needs more compute every quarter even though application traffic has not increased…
Enterprise applications rarely become slow because a database suddenly becomes incapable of returning data. Performance usually deteriorates gradually as more services, users, queries, API calls, and personalization requirements converge on the same data layer. A database that performs comfortably at normal traffic can become the bottleneck during campaign launches, market events, customer onboarding peaks, or…
Enterprise web applications rarely become slow because of one badly written function or one undersized server. Performance usually deteriorates gradually as applications accumulate services, database calls, third-party integrations, client-side JavaScript, authentication checks, analytics, regional dependencies, and years of architectural decisions. That creates a difficult problem for engineering leaders. Adding infrastructure can increase capacity without making…
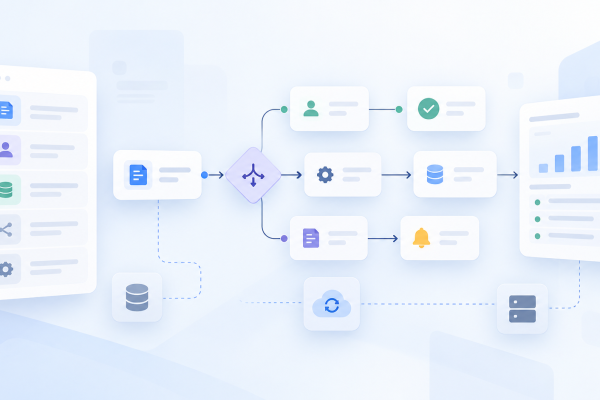
For large enterprises, the argument for building business operations without waiting for traditional development teams is easy to understand. Finance needs a new approval workflow. Operations wants to replace spreadsheets with an internal application. Customer teams need data from three systems in one interface. Engineering already has a backlog filled with customer-facing products, modernization work,…
Legacy applications rarely become security liabilities overnight. Vulnerabilities accumulate through outdated dependencies, undocumented integrations, inconsistent access controls, and architectural decisions that no longer match current security requirements. For enterprise engineering teams, the challenge extends beyond finding defective code. They must determine which weaknesses expose production systems, which can be corrected safely, and which require architectural…
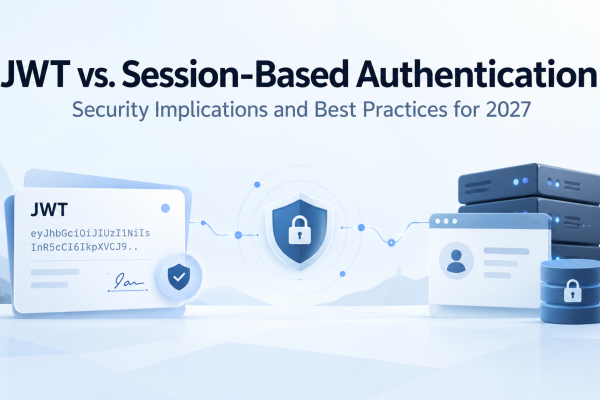
Enterprise authentication has become more complicated than deciding whether applications should use JSON Web Tokens (JWTs) or server-side sessions. With organizations operating distributed APIs, mobile applications, cloud infrastructure, and multiple identity providers, authentication decisions directly affect security, scalability, and incident response. For engineering leaders planning their 2027 architecture, the challenge is maintaining consistent access controls…
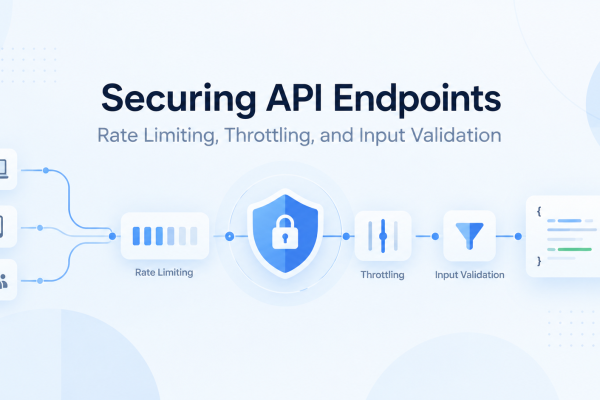
Enterprise APIs connect customer applications, internal platforms, payment systems, cloud infrastructure, and third-party services. As these integrations grow, engineering teams face a challenge: keeping APIs accessible to legitimate users without exposing infrastructure to abuse, excessive consumption, or malicious requests. Authentication alone cannot solve this problem. An authenticated user can repeatedly invoke expensive database queries, submit…
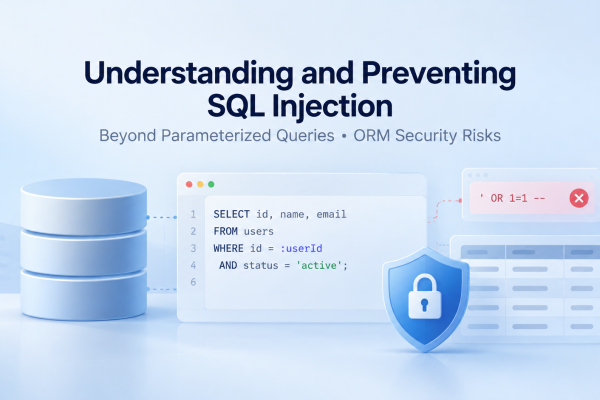
SQL injection remains a serious enterprise security risk despite widespread adoption of Object-Relational Mapping (ORM) frameworks and parameterized queries. Modern development teams rely on Hibernate, Entity Framework, Prisma, Sequelize, and SQLAlchemy to simplify database access and reduce common coding vulnerabilities. However, these abstractions do not eliminate every opportunity for attackers to manipulate SQL execution. According…
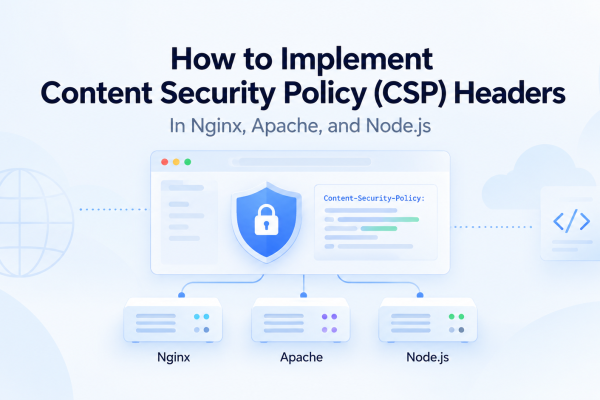
Content Security Policy often enters an enterprise backlog as a security-header task. It rarely stays that simple. A modern enterprise application may load JavaScript from multiple internal domains, analytics platforms, identity providers, CDNs, customer-support tools, payment systems, experimentation platforms, and increasingly AI-enabled services. Add legacy inline scripts and multiple deployment layers, and a CSP that…